One overlooked device can put a Middle East factory at risk
Security executives at GISEC Global 2026 warn that connected infrastructure is turning cyber weaknesses into risks to production, safety and revenue.
Key takeaways
- Connected cameras, access controls and industrial equipment can turn cyber weaknesses into operational disruptions.
- Security executives say fragmented ownership leaves companies without a complete view of connected assets.
- Khaleej Times cited projections of a $20 billion–$40 billion Middle East cybersecurity market by 2030.
- Tenable’s Gavin Millard warned that AI-assisted exploitation can outpace enterprise repair cycles.
- Executives urged companies to prioritise assets and attack routes with the greatest implications for safety and business continuity.
A surveillance camera missing from a company’s records can become more than a security blind spot. It can help put an entire site out of action. That is the warning from Meriam ElOuazzani, Censys vice-president for the Middle East, Turkey and Africa, as businesses connect more of their physical operations to digital networks, according to Khaleej Times.
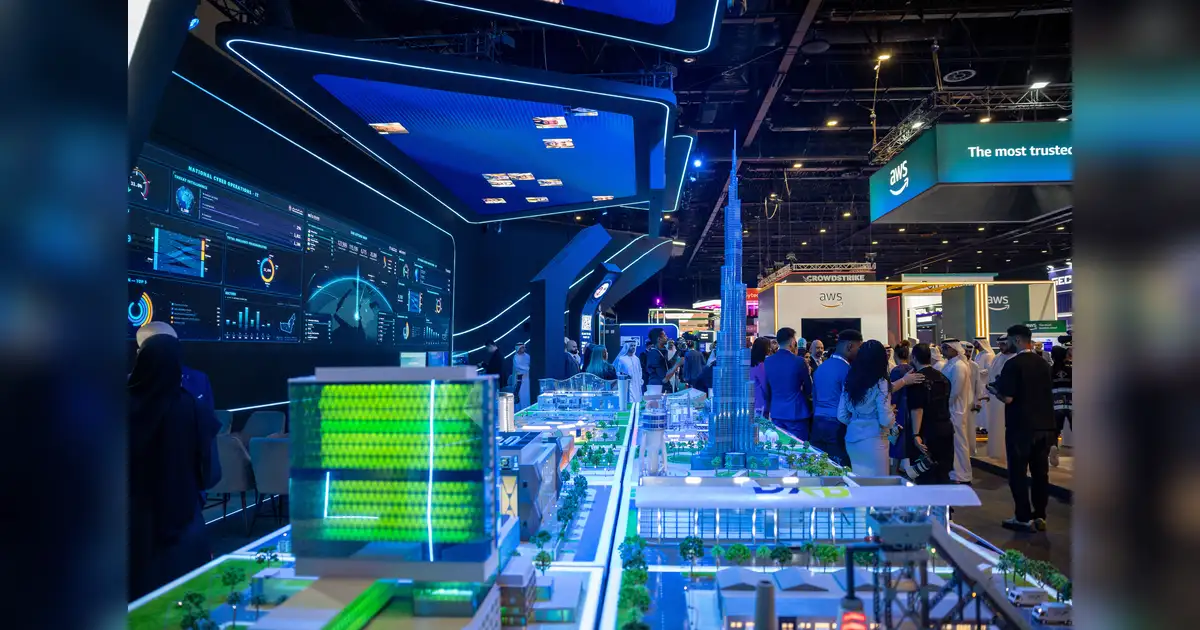
The newspaper’s coverage of GISEC Global 2026 points to a widening business challenge: protecting information is no longer enough. Investments in artificial intelligence, cloud computing, smart cities and industrial automation are bringing office systems, production equipment and building controls closer together. A weakness in one part of that chain can threaten output, safety, revenue and customer trust. Security executives say companies need to manage those exposures together, rather than leave them with separate departments.
Connected assets, divided responsibility
ElOuazzani said Saudi Vision 2030 and the UAE’s digital transformation agenda are accelerating that integration. Surveillance systems, access controls and industrial infrastructure are joining environments previously associated with financial and customer information. Khaleej Times reported projections putting the Middle East cybersecurity market at between $20 billion and $40 billion by 2030. Yet the practical test for security chiefs, ElOuazzani argued, is whether they can make joined-up decisions across digital systems, physical assets and outside suppliers.
Gavin Millard, vice-president for intelligence at Tenable, identified a basic obstacle: even large companies with established security programmes often lack a complete list of connected equipment. Engineers oversee operational technology, or OT—the systems that control physical equipment. Facilities teams manage building security, while other teams control cloud services. That split can leave nobody with a full view. In a port, utility or smart city, he said, an exposed online service combined with excessive access permissions can affect a pump, barrier or entry-control system, not just data.
Connected equipment belongs within the security remit, whatever department owns it, Tenable’s Gavin Millard argued.
Ned Baltagi, managing director for the Middle East, Africa and Turkey at SANS Institute, said the stakes are especially high for businesses built around production lines, power grids or industrial plants. Disruption to OT directly affects revenue. He cited independent financial models estimating worldwide losses from OT cyber incidents in the hundreds of billions of dollars in severe disruption years. Much of the damage, he said, comes from stopped operations, interrupted supply chains and precautionary shutdowns rather than the initial breach.
The race between exploits and repairs
Artificial intelligence adds another layer to the problem. As businesses use it for predictive maintenance—anticipating equipment failures—and production improvements, security becomes a matter of reliability and safety. Sujoy Banerjee, regional business director at ManageEngine, called for a shared view of assets, access rights and linked systems. Bachir Moussa, regional vice-president for EMEA South at Nozomi Networks, similarly highlighted industrial controls and connected devices as places where digital incidents can cause physical disruption.
Millard said advances in frontier AI can help uncover critical software flaws and produce working ways to exploit them within hours, while company patching cycles often run from 30 to 90 days. His warning was that teams can stay busy clearing alerts without addressing the exposures that matter most to the business.
The next test, in Millard’s view, is how security leaders set priorities over the coming 12 to 18 months. He advised identifying the ten assets whose compromise would most threaten continuity or safety, tracing the routes an attacker could take to reach them, and fixing those exposures first. For companies expanding connected infrastructure, the issue to watch is whether departmental boundaries give way to that shared view of operational risk.
Sources
Investing involves risk. TGC value can fall. This is not investment advice.
Comments
No comments yet — be the first.